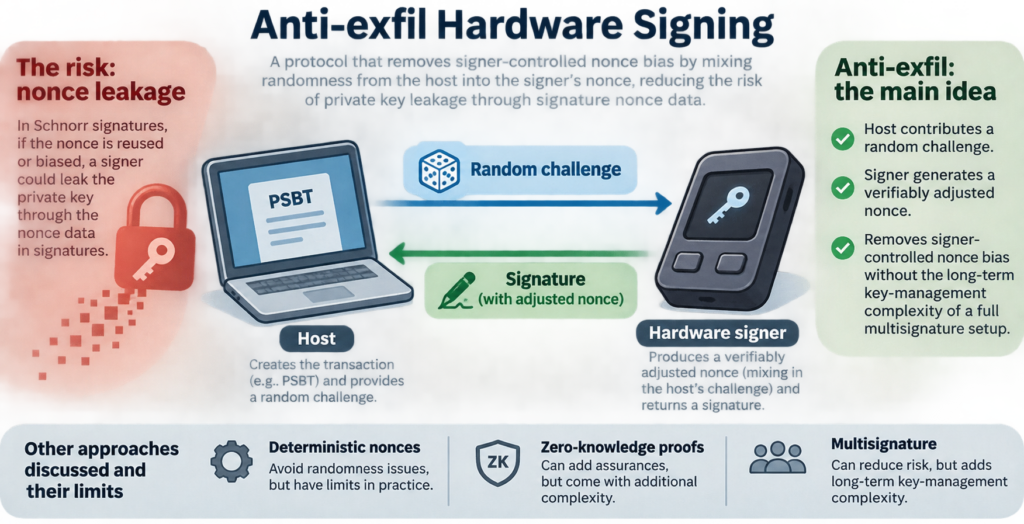
In a transcript published on November 15, 2026, Andrew Poelstra explains a risk in hardware signing: a signer could leak a private key through the nonce data it produces for signatures. Starting with the Schnorr signature formula, he discusses why nonce reuse or bias matters and the limits of deterministic nonces, zero-knowledge proofs and multisignature approaches as safeguards.
The approach he describes, called anti-exfil, has the host contribute a random challenge while the signer produces a verifiably adjusted nonce. Poelstra presents this as a way to remove signer-controlled nonce bias without adding the long-term key-management complexity of a full multisignature setup. The transcript also covers Blockstream Jade’s implementation, its PSBT interaction and an earlier application involving OpenTimestamps. It is an explanation of the protocol and its implementation, not evidence that every hardware signer uses it.